

The rise of AI has sparked newer, more sophisticated ways to attack any website, not just online stores. Regrettably, e-commerce sites remain the primary target because that is where billing details, customer data, and money live. PrestaShop has detected a new phishing campaign impersonating the official PrestaShop billing team. Thanks to swift alerts from several community members and partner agencies, the attack vector has been mapped out and preventive measures have been put in place.
As always, if you are already one of our PrestaShop clients, you have nothing to worry about—we have already taken care of everything. But if you aren’t yet (though you really should be!), here is a breakdown of how the attack works so you can prevent potential chaos.
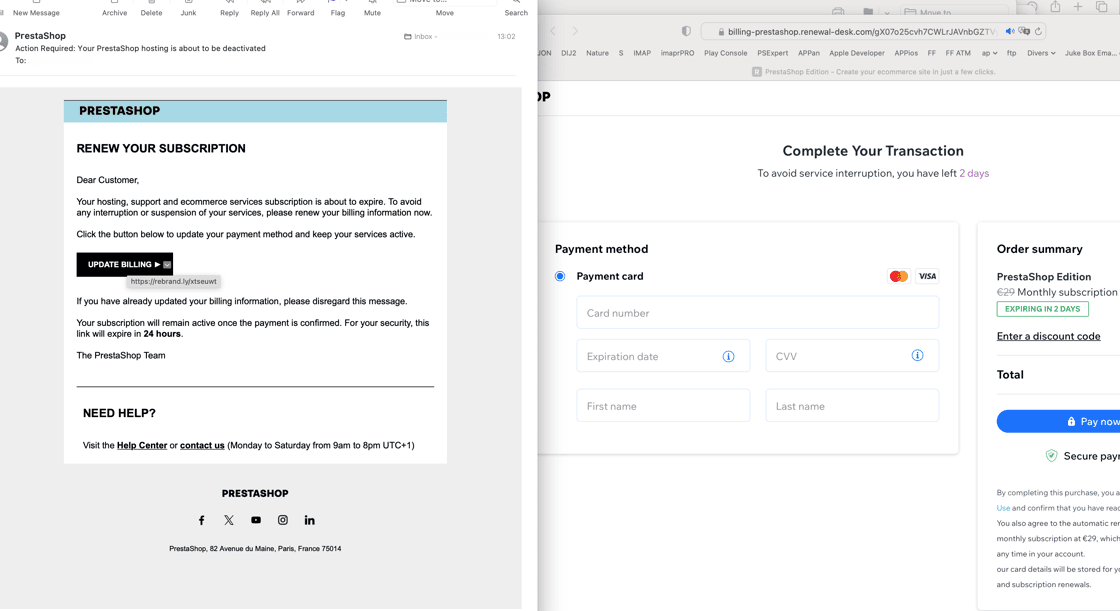
A screenshot showing what phishing looks like in action.
How does this phishing attack work?
Cybercriminals are sending fraudulent emails pretending to be from PrestaShop’s accounts payable or billing department, attempting to request payments or harvest login credentials. If you work with Ninja Labs or another agency, ignore these messages and contact your agency straight away so they can guide you.
There is currently no evidence of data leaks or security breaches within PrestaShop’s databases. Since development and support agencies appear to be the main target, all signs point to attackers using public lists of partner agency contacts rather than an internal customer database.
Security recommendations for PrestaShop agencies and merchants
Whether you run your own online store or provide PrestaShop maintenance services to clients, we strongly recommend taking these immediate precautions:
- Inform your clients: Share this security alert with your clients so they remain vigilant against suspicious invoices or unusual emails.
- Verify the sender: Always check the official domain on incoming email addresses before clicking any links or downloading attachments.
- Follow security best practices: Keep in mind that PrestaShop will never ask for your passwords or sensitive banking details via unverified emails.
What should you do if you spot a suspicious email?
If you encounter a variation of this fraudulent email or suspect a merchant has been compromised:
- Do not interact with the message or share any financial information.
- Report it immediately to the official team via the PrestaShop Care Centre.
Remember: if you want total peace of mind, your best bet is to leave your online store’s security in the hands of professionals. Get in touch, tell us a bit about your website, and let’s see how we can help.